

You deserve
to be hacked.
Successful companies like yours are constant targets for attackers. Those who take security seriously don’t just test their defenses once a year.
They subscribe to CovertSwarm.
Can your security program survive an attack?
You bought the tests, the tools and the scanners. You tell them where to look, and they’ll tell you what they found. None of them can tell you what will break your business.
Threat actors target your whole organization. Your people, systems and suppliers. You don’t need more findings. You need proof of where you really stand. For your board. For your regulator. For yourself.
How confident are you?
The only way to be confident is to face a real attacker.
We become the threat. CovertSwarm is a team of elite ethical hackers augmented by agentic tools, that thinks, acts and strikes like a real attacker.
Your Swarm attacks your whole organization across physical, social, and digital environments within safe guardrails, proving how far a real attacker could go and showing you how to fix the weaknesses.
One simple subscription gives you direct team access and board-ready evidence of where you stand.
Over 100 security leaders subscribe. Are you ready? Let’s find out.
It takes a Swarm to outpace threats.
While you plan your next test, attackers are probing everything: your systems, your people, and your suppliers. They don’t care about scopes or findings. They’re focused on objectives.
And they won’t send a nice PDF when they’re done.
Relentless adversarial pressure.
Forget rigid scopes and waiting weeks for a report. We give you a relentless adversary, attacking, probing, and exposing weaknesses before real attackers do. And if we can’t break in, you’ll know your security investments are working.
The closest thing to the threats you face every day.
Persistent by design.
A test ends with a report. Your Swarm doesn’t stop there. Within your agreed guardrails, they’ll continue to attack until they reach their objectives.
Your own APT, built to target you, that changes and adapts with you.
One subscription is all you need.
Digital. Social. Physical. Compliance. Regulatory testing. Get it all in one simple subscription for less than the cost of a single security hire.
Simpler billing and less procurement so you can keep moving faster.
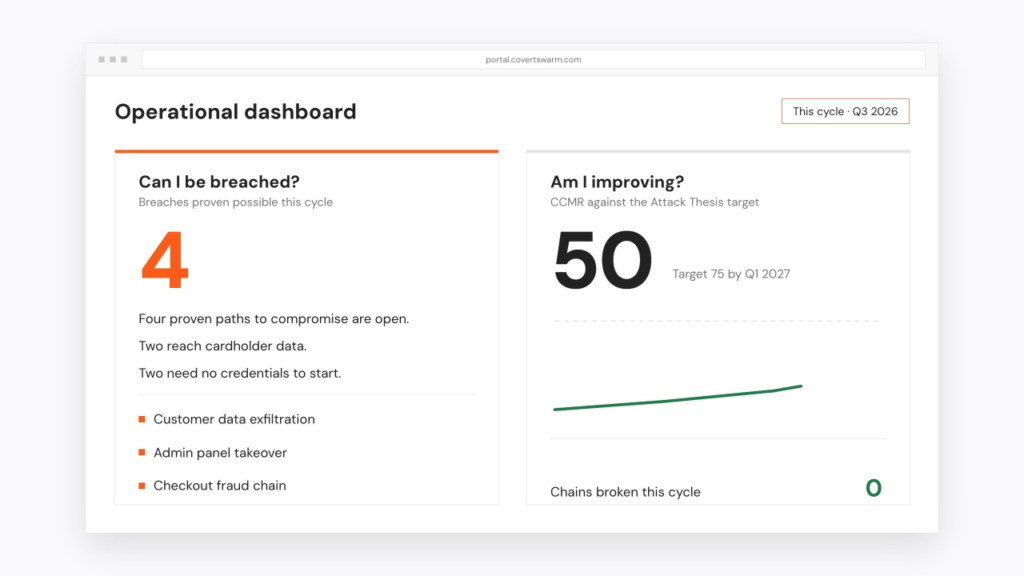
Your direct line to the Swarm.
See what your Swarm is targeting, what they have proven and what needs fixing. One shared view of the attacks and your response, all in the CovertSwarm portal.
Stories from the Swarm
These stories are real, but the names are redacted. We’ll tell you how we uncovered the threats no one else could see, and why constant cyber attack is the best way to outpace cyber threats.
Use Cases
Your biggest security problems each have an attacker behind them. Constant Cyber Attack™ becomes that attacker, so you can see what holds and what to fix.
-
Regulatory and compliance readiness
Compliance is mandatory. Attackers are relentless. Get threat-led, regulator-aligned testing while strengthening real-world resilience.
-
Prove the effectiveness of your security investments
You’ve invested in security. Now demand proof it works. CovertSwarm attacks your technology, people and processes to reveal what stops an adversary, what fails and where to focus next.
-
Secure your AI and agentic systems
CovertSwarm attacks your agents and AI apps to show how attackers could breach them, and what they could reach.
-
Improve resilience against AI-enabled attacks
CovertSwarm prepares you to meet the pace and intensity of AI-enabled attackers.
-
Unknown risk discovery
CovertSwarm strengthens your security posture by continuously attacking, exposing, and mapping currently unknown risks.
Latest posts
Apache HTTP Server – mod_http2 Remote Code Execution (CVE-2026-119618)
A race condition in Apache HTTP Server’s mod_http2 lets an unauthenticated remote attacker corrupt the heap and potentially take control of the server process. Versions 2.4.55 through 2.4.70 are affected when HTTP/2 is enabled, including servers already updated for CVE-2026-23918. Update to 2.4.71 or your distribution’s fixed package, or disable HTTP/2 until you can.
Your red team isn’t testing the fridge
In October 2026, attackers remotely shut down refrigeration in hundreds of European supermarkets through outdated, internet-exposed controllers. Most red team engagements would never have caught it, because fridges, HVAC and building systems sit outside the usual scope. Here are four steps to bring OT security testing into your program.
Stop testing.
Start knowing.
You’ll know exactly where you stand, and you’ll be able to prove it. To your board, your regulator, and yourself.
Transform to a proactive, continuous offensive security program
Your budget is aimed at the risk that matters, not the one you were handed
You show the board what security prevented, not a request for more
Security clears the way for the business to move faster
You enter the boardroom in command
It starts with a 30-minute Attack Discovery call.
No access to your systems required.